Crypto Compliance, KYC/AML & Regulatory Integration in Köln
Regulatory scrutiny on crypto businesses keeps rising. Hurain Technologies integrates KYC/KYB onboarding, AML transaction monitoring, sanctions screening and FATF Travel Rule messaging into crypto exchanges, wallets and payment platforms, using a jurisdiction-aware rule engine built to work alongside licensed legal counsel.
Köln is the largest city in North Rhine-Westphalia, Germany, home to around 1.0 million people. Crypto Compliance & KYC/AML for Köln businesses has to account for SEPA Direct Debit and PayPal payments, VAT (USt) 19% and the EU General Data Protection Regulation (GDPR) and the BDSG. Our team works remotely from India, available 24/7 (India (IST) is 4h 30m ahead), with one project manager and full source-code ownership.
Quick answer
Who provides crypto compliance & kyc/aml in Köln?
Hurain Technologies delivers crypto compliance, KYC/AML & regulatory integration for companies in Köln, Germany, available 24/7, with builds that support SEPA Direct Debit and PayPal, VAT (USt) 19% and the EU General Data Protection Regulation (GDPR) and the BDSG. Founder Shahnavaz Syed leads a DBA team, development team and hosting team with 15+ years of experience each, so your crypto compliance & kyc/aml project is designed, built and hosted by the same accountable group. Pricing starts at USD 15–40 per hour; final charges and timeline are set after we confirm your requirements, and depend on your budget and the team members assigned to the project.
 Reviewed by Shahnavaz Syed, Founder · Last updated
At a glance
- Since 2010
- Engineering software
- 24/7
- Team availability
- USD 15–40/hr
- Starting rate
- 10 minutes
- Typical first response
One project manager, milestone-based scopes, full source-code ownership and a demo within 24 hours of our meeting.
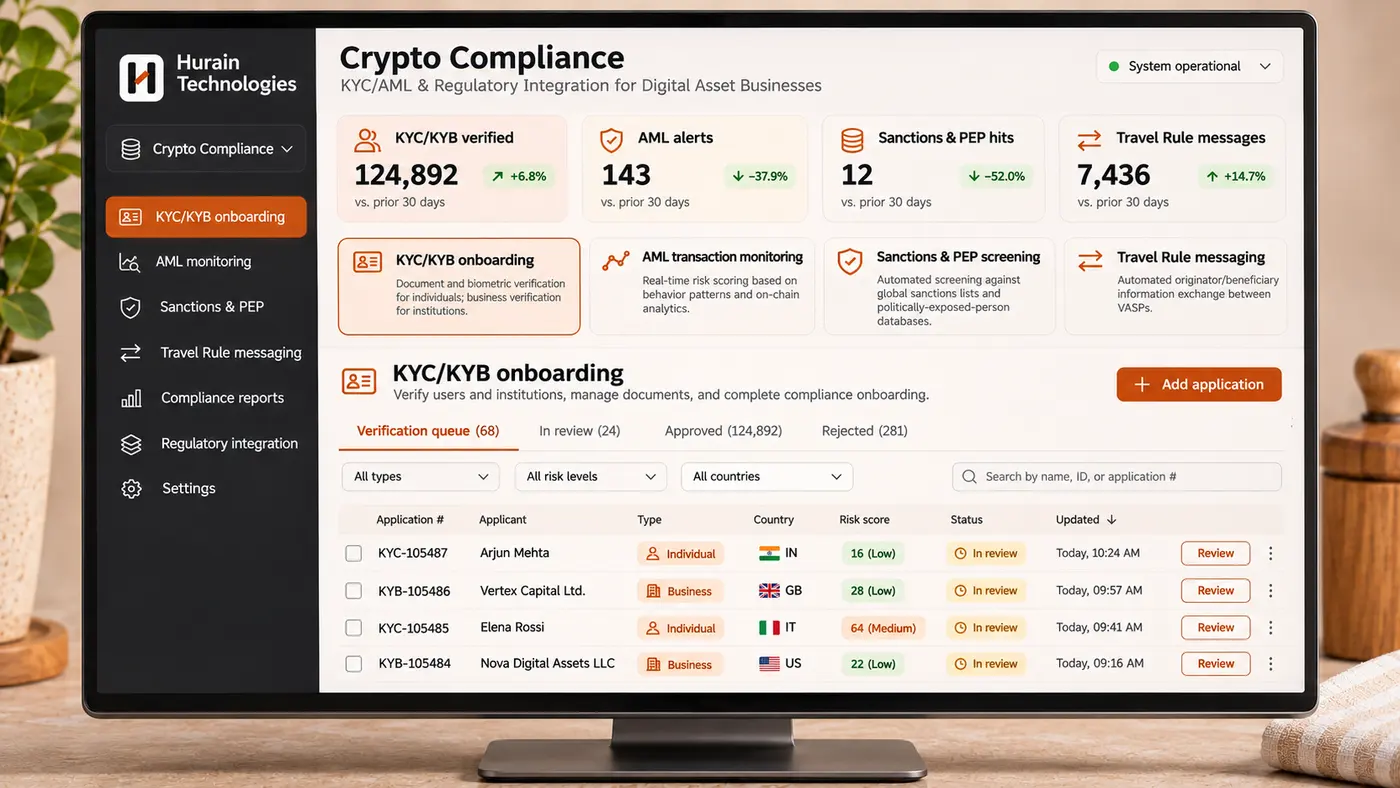
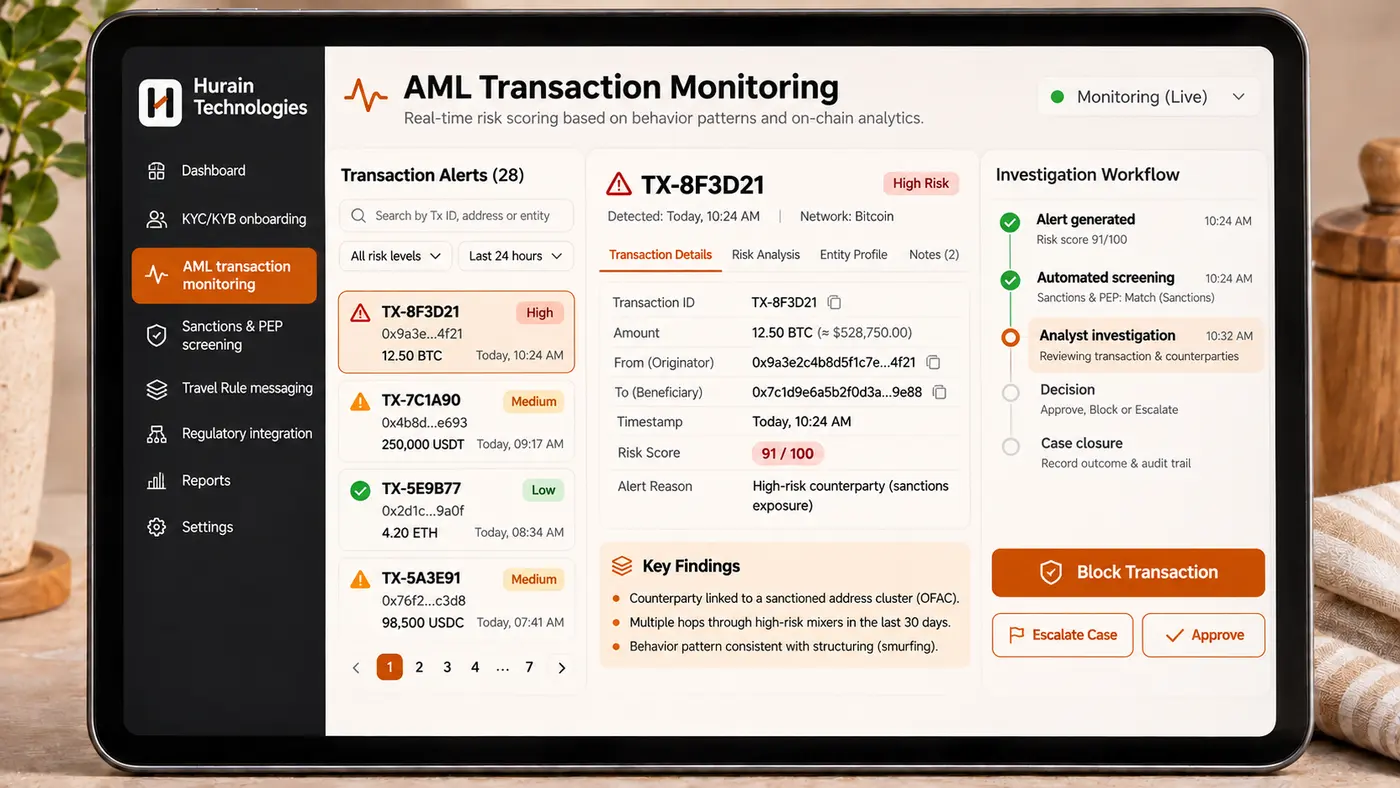
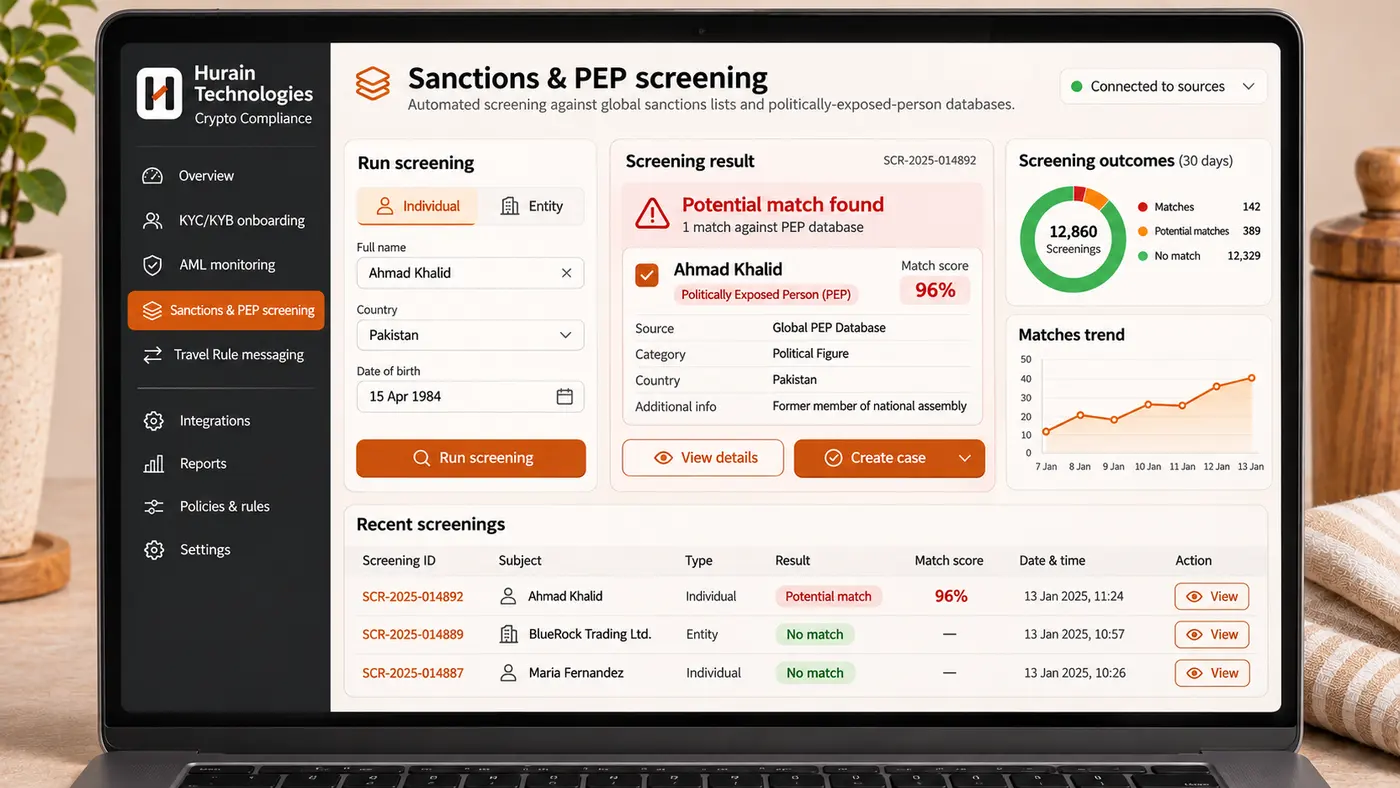
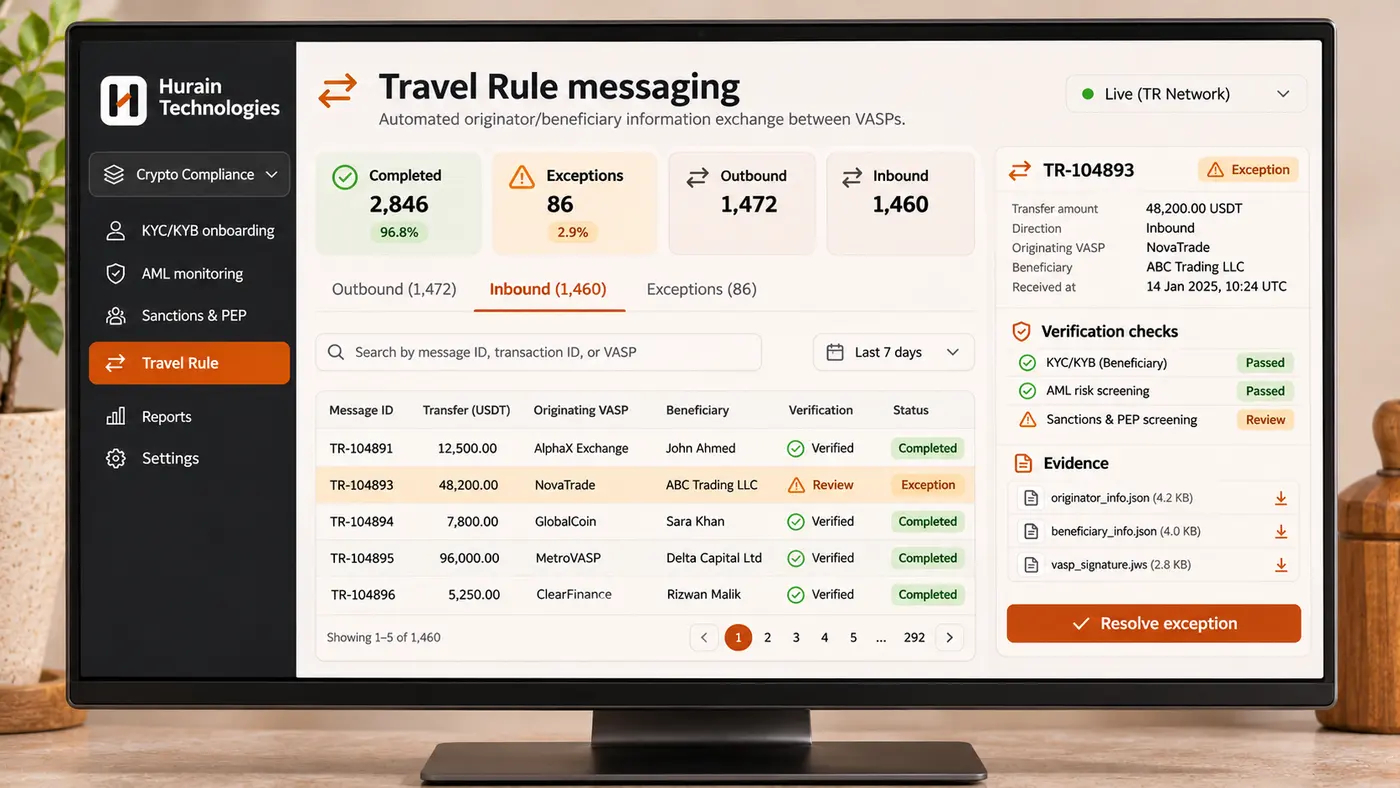
Product screens
Crypto Compliance & KYC/AML screens we would build for a company in Köln
Three more working screens from a typical build, one at a time so the detail stays readable: a step-by-step workflow, the configuration console and the reporting screen. Swipe or use the arrows. Sample data is fictional.
Local blueprint
Example: how we would launch crypto compliance & kyc/aml in Köln
Illustrative example, not a client case study
Köln has about 1,024,621 people in Germany, where businesses price in EUR.
A team in Köln should plan for Android-first: many users are on mid-range and low-end phones, so the first release is tested on the devices your customers use here.
Interfaces and support content can ship in German.
Local launch checklist for Köln
- Week 1: agree the first-release scope for Köln (kyc onboarding flow with vendor integration; sanctions and wallet screening) and who signs it off.
- Payments: connect SEPA Direct Debit, PayPal and Klarna and settle in EUR; test failed, refunded and reversed payments.
- Tax and invoices: build in VAT (USt) 19%; every invoice and report follows it.
- Data protection: choose the hosting region and retention period under the EU General Data Protection Regulation (GDPR) and the BDSG.
- Localisation: German, +49 phone validation, local date, number and address formats.
- Regulator check: confirm with counsel whether BaFin rules apply to your model before launch.
- Release: Google Play first, App Store second; a pilot with a small group in Köln, then widen.
- Support: Köln is on UTC+1; our team covers your business day and answers every enquiry within 10 minutes.
Rules to plan for in Köln, Germany
| Area | What applies | How the build handles it |
|---|---|---|
| Tax and invoicing | VAT (USt) 19% | Tax lines, rounding and reports follow the local rule; confirm rates with your accountant. |
| Privacy and data | the EU General Data Protection Regulation (GDPR) and the BDSG | Consent, retention, access and deletion flows; hosting region agreed with you. |
| Payments | SEPA Direct Debit, PayPal, Klarna and Cards & Apple Pay | Only methods your customers use; failure, refund and chargeback handling are built in. |
| Sector regulator | BaFin | We plan audit logs and reports with your counsel; licences remain your responsibility. |
| Consumer protection | Online-sales and refund rules in Germany | Clear prices, cancellation and refund screens and receipts; exact wording is confirmed with local counsel. |
| Language and accessibility | German | readable contrast and keyboard use on web; larger text on mobile. |
Planning prompts, not legal advice. Confirm rates, licences and wording with local counsel and your accountant.
Launch and delivery zones
- Zone 1: Köln
Pilot with a small group, fix what real use shows, and measure the numbers you agreed. - Zone 2: Berlin and nearby cities
Open next in stages, with local payment, language and support settings checked per city. - Zone 3: the rest of Germany
Wider rollout once the pilot numbers and support load are stable.
Local risks and how they are handled
| Risk | What we do |
|---|---|
| Low adoption of the payment method you launch with | Start with SEPA Direct Debit and PayPal, add the next one after the pilot data, and keep a fallback. |
| Data-residency or privacy objections from local customers | Hosting region and retention are agreed up front under the EU General Data Protection Regulation (GDPR) and the BDSG; deletion and export are built in. |
| Slow or low-end Android devices | Written device matrix, tests on real devices, small downloads and offline-tolerant screens. |
| Licensing or reporting duties under BaFin | Counsel confirms the model early; the product keeps the logs and reports they ask for. |
| Support gaps across time zones (Köln is on UTC+1) | 24/7 shifts cover your business day; urgent issues are answered within 10 minutes. |
| Scaling beyond Köln | Pilot in Köln, check the numbers, then open Berlin and Hamburg in stages. |
Try it: a clickable prototype of kyc and identity verification (sample data) shows what a Köln team would use.
Localised for your market
Crypto Compliance & KYC/AML in Köln: local requirements we build for
Currency, tax, payments, data protection and 24/7 support — planned into the project from the first sprint.

Currency & pricing
Prices, invoices and reports in Euro (EUR), with the transaction currency and FX rate stored on every record for cross-border sales.
Tax (VAT / GST)
Germany applies VAT (USt) 19%. We build tax-correct pricing, invoice fields and exportable tax reports; your accountant confirms treatment for your products.
Payments
Customers in Köln expect SEPA Direct Debit, PayPal, Klarna and Cards & Apple Pay — integrated with automatic reconciliation.
Data protection
Personal data is governed by the EU General Data Protection Regulation (GDPR) and the BDSG. We build consent, encryption, access logs and in-region hosting where required.
24/7 availability
Köln is on UTC+1 (India (IST) is 4h 30m ahead). Our team works 24/7, so your full business day and any out-of-hours incident are covered.
Delivery timeline
Discovery starts within 5 business days of a signed proposal. Most crypto compliance & KYC/AML engagements ship a first production release in 6–14 weeks, with demos every two weeks.
The Challenge
Problems we see teams struggling with
Multiple regulatory frameworks
Different countries have different KYC tiers, transaction limits, and reporting obligations. In Germany this also means working to BaFin and the EU General Data Protection Regulation (GDPR) and the BDSG.
Manual compliance processes
KYC verification and sanctions screening slow user onboarding without automation. In Germany this also means working to BaFin and the EU General Data Protection Regulation (GDPR) and the BDSG.
Travel Rule messaging
Cross-VASP originator/beneficiary information exchange is required but complex to implement. In Germany this also means working to BaFin and the EU General Data Protection Regulation (GDPR) and the BDSG.
Licensing readiness
Missing audit trails, access controls, or reporting capability can block licensing applications. In Germany this also means working to BaFin and the EU General Data Protection Regulation (GDPR) and the BDSG.
False positives overwhelming compliance teams
Poorly tuned sanctions screening generates enough false matches that genuine risk gets lost in the noise, and analysts burn out clearing routine false alarms. In Germany this also means working to BaFin and the EU General Data Protection Regulation (GDPR) and the BDSG.
On-chain risk exposure going undetected
Without chain-surveillance tooling, a platform can unknowingly process funds that touched a sanctioned address several hops back in the transaction history. In Germany this also means working to BaFin and the EU General Data Protection Regulation (GDPR) and the BDSG.
Our Approach
What our crypto compliance & kyc/aml work covers in Köln
KYC/KYB onboarding
Document and biometric verification for individuals; business verification for institutions. For Köln we map the controls to BaFin and the EU General Data Protection Regulation (GDPR) and the BDSG.
AML transaction monitoring
Real-time risk scoring based on behavior patterns and on-chain analytics. For Köln we map the controls to BaFin and the EU General Data Protection Regulation (GDPR) and the BDSG.
Sanctions & PEP screening
Automated screening against global sanctions lists and politically-exposed-person databases. For Köln we map the controls to BaFin and the EU General Data Protection Regulation (GDPR) and the BDSG.
Travel Rule messaging
Automated originator/beneficiary information exchange between VASPs. For Köln we map the controls to BaFin and the EU General Data Protection Regulation (GDPR) and the BDSG.
On-chain analytics
Connect chain-surveillance tooling to flag exposure to high-risk wallets. Our 24/7 team schedules this work around Köln (UTC+1) business hours.
Regulator-ready reporting
Audit trails and reports formatted for the regulators overseeing your license. For Köln we map the controls to BaFin and the EU General Data Protection Regulation (GDPR) and the BDSG.
Screening tuning to reduce false positives
Match-scoring calibration that reduces false-positive alert volume so genuine risk doesn't get lost in analyst fatigue. Our 24/7 team schedules this work around Köln (UTC+1) business hours.
Technology
Tech stack we work with
Compliance
Backend
Rules Engine
Monitoring
Köln project brief
How a crypto compliance & kyc/aml project for Köln would run
Köln has around 1.0 million people and sits on UTC+1; India is 4h 30m ahead. Our team works 24/7 from India, so stand-ups and demos can be scheduled in Köln business hours rather than ours.
For blockchain and crypto products the first question in Germany is licensing and onboarding: BaFin is the body to check with your counsel, and we build KYC/AML, transaction monitoring and audit logs so those checks can be evidenced. Customer data must also follow the EU General Data Protection Regulation (GDPR) and the BDSG.
Teams in nearby Germany cities such as Düsseldorf (about 34 km away), Duisburg (about 57 km away) and Essen (about 57 km away) follow the same remote delivery model, so Köln clients can ask us for references from comparable markets.
Business value
What Crypto Compliance, KYC/AML & Regulatory Integration in Köln does for your business
Benefits for your company
- Meet licence conditions. KYC, sanctions screening, transaction monitoring and Travel Rule flows that regulators expect from VASPs.
- Faster, cleaner onboarding. Automated identity checks reduce manual reviews and the time before a customer can transact.
- Audit trail by default. Every decision is logged for regulators, banking partners and internal audit.
How it can earn or save money
- Keep banking relationships. Strong compliance keeps bank and payment partners willing to work with you.
- Serve regulated markets. Compliance tooling opens licensed markets and higher-value customers.
- Lower compliance cost per user. Automation reduces the analyst hours spent per customer onboarded.
Illustrative revenue and saving lines, not guaranteed results: outcomes depend on your market, licences and execution.
How we work
How we deliver Crypto Compliance & KYC/AML in Köln, Germany
Every crypto compliance & kyc/aml engagement in Köln, Germany follows the same staged, quality-gated process — shaped around your requirements and Köln's market. You see progress every day, review it every week, and give written sign-off at every milestone before any payment is due.
- 01
Discover
Scope signed off- Token & protocol workshops
- Chain & custody selection
- Regulatory scoping
- Signed scope
- 02
Design
Threat model OK- Contract architecture
- Tokenomics & access roles
- Key management design
- Threat model
- 03
Build
Testnet accepted- Solidity / Rust sprints
- Testnet deployments
- Gas optimisation
- Demo every sprint
- 04
Secure & Test
Audit cleared- Unit, fuzz & invariant tests
- Independent audit coordination
- Audit fixes verified
- UAT on testnet
- 05
Deploy
Mainnet live- Mainnet deploy via multisig
- Contract verification
- Monitoring & alerts
- Go-live checklist
- 06
Handover
Keys transferred- Role-based sessions
- Recorded walkthroughs
- Admin & ops runbooks
- Documentation handover
- 07
Support
Monitoring live- Dedicated engineer
- SLA helpdesk
- Patches & upgrades
- Quarterly reviews
Client sign-off at every milestone — you approve the working result before you pay.
You always know what was done today — and what happens next
With about 5.5 shared working hours a day between Köln and our team in India, questions are answered the same day and your update is waiting for you at around 2:30 PM.
Every working day, around 2:30 PM Köln time
- What was completed today
- What is planned for tomorrow
- Blockers and decisions needed from you
- Links to builds you can try
Every Friday, with a live call in your business hours
- Features completed and demo recordings
- Progress against the current milestone
- Risks, open questions and change requests
- Plan and priorities for next week
End of every sprint and milestone
- Working software demonstrated live
- Your feedback captured in the backlog
- Quality-gate checklist shared
- Written sign-off before any payment
What we build in for Köln
Local requirements are part of the scope from the Discover stage — not retrofitted before launch.
Data protection
Data handling, consent and retention designed for the EU General Data Protection Regulation (GDPR) and the BDSG.
Regulator
Controls, reports and audit trails prepared with BaFin expectations in mind, alongside your local counsel.
Language & currency
German interfaces and content, EUR pricing, invoices and number formats.
Time zone
Köln is on UTC+1; India (IST) is 4h 30m ahead. Calls, demos and sign-offs are scheduled in your business hours.
Payment plan
Pay only for work you have accepted
Milestones are customised to your requirements — six or more is typical, and delivery time is agreed around your scope. Every payment after the advance is released only after you have seen the working result and given written sign-off. Here is an example plan:
| Payment | Milestone & acceptance | Share |
|---|---|---|
| Advance | Contract signing Signed contract; protocol workshops and chain selection. | 10% |
| Milestone 1 | Architecture approved Contract architecture, tokenomics and threat model signed off. | 15% |
| Milestone 2 | Testnet v1 First contracts deployed and demonstrated on testnet. | 15% |
| Milestone 3 | Feature-complete testnet All contracts, dApp and admin flows running end to end. | 15% |
| Milestone 4 | Audit passed Independent audit done; every finding fixed and re-verified. | 15% |
| Milestone 5 | Mainnet launch Multisig mainnet deployment and contract verification. | 15% |
| Milestone 6 | Handover Monitoring, runbooks, training and documentation handed over. | 15% |
| Total | 100% | |
- Number of milestones and splits set around your scope
- Every milestone is a working, demonstrated result
- No payment is due until you sign off
Warranty & annual support
Protected after launch — warranty and annual support for your Crypto Compliance & KYC/AML project in Köln, Germany
Go-live is where your crypto compliance & kyc/aml product starts earning — so we stay accountable for it. Every project includes a free 90-day defect warranty. After that, the same team that built it keeps it secure, updated and running in Köln business hours on a fixed annual fee agreed up front — no open-ended hourly billing, no surprise invoices.
Included free
90-day warranty
Any defect found in the first 90 days after go-live is fixed free of charge.
- Every delivered feature covered
- Fixes tested and deployed to production
- Same engineers who built it
Fixed-cost annual package
30% of project cost
per year for Annual Support & Maintenance, with a dedicated developer assigned to your crypto compliance & kyc/aml platform. A fixed price, known in advance.
| Service | Included in the annual package |
|---|---|
| Dedicated developer | One named developer assigned to your product for fixes, enhancements and optimisation. |
| Bug fixes & security patches | Critical issues resolved within 24 hours; standard issues within 5 business days. |
| Upgrades & new releases | Framework, library and platform updates plus new versions of what we built, at no additional cost. |
| Helpdesk | Email and phone support for your team and administrators; 4-hour response for critical issues. |
| Backup monitoring | Daily backup checks and a quarterly restore test. |
| Security review | Periodic audit-trail review and security configuration check. |
| On-chain monitoring | Contract events, admin actions and unusual transactions watched with alerts. |
| Network & node upgrades | Hard forks, RPC and library changes tracked; contract upgrades run through the multisig. |
| Sanctions-list updates | Screening lists refreshed and matching rules re-tested after each update. |
| Köln business-hours coverage | Helpdesk, calls and planned maintenance scheduled around Köln business hours (UTC+1); critical issues escalated immediately. |
| Local compliance updates | Changes to the EU General Data Protection Regulation (GDPR) and the BDSG and BaFin guidance tracked and reflected in the product. |
Source code & IP ownership
100% of the source code and IP is owned by you
For every custom crypto compliance & kyc/aml project in Köln, Germany, upon full and final payment the complete source code and intellectual property are transferred to you — so you can host, maintain and enhance the system with any developer.
- Smart-contract source, tests and deployment scripts
- Contract ownership and multisig admin keys transferred to you
- Audit reports and dApp / admin source code
- Complete Git repository with full commit history
- Database schemas, migrations and seed data
- Configuration, CI/CD and deployment scripts
- API documentation and a deployment guide
No lock-in
No forced upgrades
No subscription trap
Your code lives in your own repository from the first commit.
Continuous enhancement
Launch is just the beginning — keep shipping with your own dedicated team
Your crypto compliance & kyc/aml platform should get better every month, not stand still after go-live. Start with one dedicated developer working on your priorities across apps, dashboards and backend — and grow to a full team of developers and support members whenever your roadmap demands it.
Dedicated team, your way
From one developer to a full team
Pricing is based on the team members you need — tell us your requirements and we will quote your team.
- Start any time after launch
- Hire developers as you need them
- Scale up, scale down or pause
What your team can take on after launch
- New screening lists and risk rules
- Faster onboarding with better document checks
- Case-management and regulator reporting automation
- New contracts, tokens or chains
- dApp and admin-panel improvements
- New wallet, bridge and exchange integrations
Need more hands? Add developers and support members as your requirements grow
Start with one person and add only the roles your crypto compliance & kyc/aml roadmap needs — each is quoted to your requirements.
Development team
Risk-rules engineer
Tunes screening and monitoring rules as risks change.
Smart-contract developer
Writes, tests and upgrades contracts in Solidity or Rust.
dApp developer
Builds the wallet-connected web interfaces for your contracts.
Backend developer
Adds the APIs, business logic and data models behind new features.
QA engineer
Writes and runs manual and automated tests before every release.
DevOps engineer
Keeps pipelines, environments and deployments fast and reliable.
Support team
L1 helpdesk support executive
First contact for your users and staff — logs, triages and resolves common issues.
L2 technical support engineer
Investigates bugs, data issues and integrations, and escalates to developers with full context.
Compliance case support
Helps analysts work alerts and cases efficiently.
On-chain operations support
Watches contracts, gas balances and admin transactions.
Wallet & transaction support
Helps users trace stuck, failed or mis-sent transactions.
Our Approach
Our approach to development methodologies
Our approach to custom software engineering draws on a range of methodologies, each selected to match the needs of your crypto compliance & KYC/AML project and your team in Köln, Germany.
Agile Scrum
Best for: Evolving products
Two-week sprints with a working demo at the end of each, so crypto compliance & KYC/AML priorities can change as you learn from users.
Kanban
Best for: Continuous delivery & support
A visual flow of small tasks with work-in-progress limits — ideal for maintenance, integrations and post-launch improvements.
Fixed-scope (Waterfall-style)
Best for: Well-specified builds
Requirements signed off up front with a fixed timeline and price — best when scope is clear and change is unlikely.
Lean MVP
Best for: New ventures
Build the smallest crypto compliance & KYC/AML release that proves demand, measure it with real users, then invest where the data points.
DevOps & CI/CD
Best for: Every project
Automated tests, infrastructure-as-code and push-button deployments so releases are frequent, reversible and boring.
Security-by-design (DevSecOps)
Best for: Regulated & high-value systems
Threat modelling, dependency scanning and code review built into each sprint rather than a pen test at the end.
Why we're different
What sets Hurain Technologies apart for Germany businesses
Plenty of agencies can build crypto compliance & KYC/AML. Here is what sets us apart for clients in Köln, Germany.
Engineering depth, not a reseller
Your crypto compliance & KYC/AML project is designed and built by our own in-house engineers — no hidden subcontracting chain between you and the people writing code.
Built for Germany, not copied from elsewhere
Payments, tax, language and data-protection requirements for Germany are part of the design from day one instead of retrofitted after launch.
Transparent, senior-led delivery
A named project lead, a shared backlog, fortnightly demos and direct Slack access to the engineers — you always know what is being built and why.
Cost advantage without cutting corners
Delivering from India gives clients in Köln, Germany senior engineering at a fraction of typical onshore agency rates, with the same code-review, testing and security standards.
You own everything
Source code lives in your repository from the first commit; IP, infrastructure accounts and documentation transfer to you in full.
We stay after launch
Monitoring, updates and a support SLA mean the team that built your product is the team that keeps it running.
Flexible engagement models
How we work with businesses in Köln, Germany
Ways to work together, depending on how your team and roadmap are set up.
Dedicated Development Team
An extended team of crypto compliance & KYC/AML engineers, QA and architects working exclusively on your product, managed day-to-day by you with our engineering leadership behind them.
Best for: Long-term products and evolving roadmaps
Fixed-Cost Delivery
A clearly scoped crypto compliance & KYC/AML build with a defined timeline and price — ideal for a well-specified MVP, integration or launch product.
Best for: MVPs and clearly defined projects
Hybrid Engagement
Keep product and regulatory decisions close to your Germany team while our specialists handle deep engineering remotely, with workshops or on-site visits at key milestones.
Best for: Enterprises and regulated businesses
Why businesses choose us
Why businesses choose Hurain Technologies
16+ years of engineering depth
Custom software engineering with in-house teams across web, mobile, cloud, AI, payments and blockchain.
Security-first by default
Encryption, least-privilege access, audit logs — and MPC/HSM custody and audited smart contracts where money is on-chain — designed in, not retrofitted.
Regulatory-aware architecture
Designed with Germany's regulatory direction in mind and built alongside your licensed local legal counsel.
Direct access, no layers
Direct Slack or Teams access to your development team during the build, and the same people for post-launch support.
Business benefits
What you gain in Germany
Faster time to market
An experienced crypto compliance & KYC/AML team with proven components means your first release ships in weeks, not quarters.
Security-first architecture
Secure from day one, rather than patched after an audit or incident.
Aligned compliance groundwork
Controls, logs and data handling built around Germany's requirements so reviews go faster.
Lower total cost of ownership
Clean, documented, tested code that your own team can maintain — plus post-launch monitoring and support.
What happens next
From your crypto compliance & KYC/AML enquiry to a working demo in Köln, Germany — in about a day
- 01Within 10 minutes
We respond to your enquiry
Send your crypto compliance & KYC/AML enquiry by form, email or WhatsApp — a few lines is enough. Our team replies within 10 minutes, any day, any time, to set up a meeting at a time that suits you in Köln.
- 02Requirements meeting
We understand your requirements
In a focused meeting we go deep on your users, features, integrations, timeline and budget, plus the payment, tax and compliance rules that apply in Köln, Germany — so we build exactly what your business needs. NDAs signed on request.
- 03Within 24 hours
You see a demo of your crypto compliance & KYC/AML
Within 24 hours of our meeting we prepare and share a demo — so you see your crypto compliance & KYC/AML taking shape before you commit to anything.
- 04As per your budget
We share a tailored proposal
A clear proposal for your crypto compliance & KYC/AML project in Köln, Germany with scope, milestones, team and timeline — shaped around your budget, with no hidden costs and no obligation.
Available 24×7 — three 8-hour shifts, every day
FAQ
Crypto Compliance & KYC/AML in Köln — FAQ
Do you work with crypto compliance & KYC/AML clients in Köln?
Which currency and taxes apply to projects in Germany?
How quickly can you start a project in Köln?
Which crypto compliance & KYC/AML company can build this for my business in Köln?
How do I choose the best crypto compliance & KYC/AML company in Köln?
Can I outsource crypto compliance & KYC/AML for Köln to an offshore team in India?
Do you build the complete crypto compliance & KYC/AML solution, or only integrate with what we already use?
We are not sure about our budget yet. Can you still help?
Do you provide dedicated development teams for companies in Köln?
What industries in Köln do you serve?
Can you help modernize our legacy banking core?
Do you build GDPR-aligned data architecture?
What is FATF Travel Rule compliance?
Which KYC/AML providers can be integrated?
Can compliance rules differ by country?
Does this speed up getting a VASP license?
Our prototypes
Working products we designed and built ourselves
Clickable prototypes our own engineers built and run on sample data, with web and mobile views, every user role and a super admin. The same team builds your crypto compliance & kyc/aml project for Köln, Germany.
Prototypes use sample data and are not client projects. See all 42 live demos or ask for a demo of your own idea.
Ready to bring crypto compliance, kyc/aml & regulatory integration to Köln?
Get a response within 10 minutes, a demo within 24 hours of our meeting, and a proposal as per your budget.